

Quickly and Easily Pass Microsoft Exam with MS-102 real Dumps Updated on Apr-2026
Realistic MS-102 Dumps Questions To Gain Brilliant Result
NEW QUESTION # 237
You configure an anti-phishing policy as shown in the following exhibit.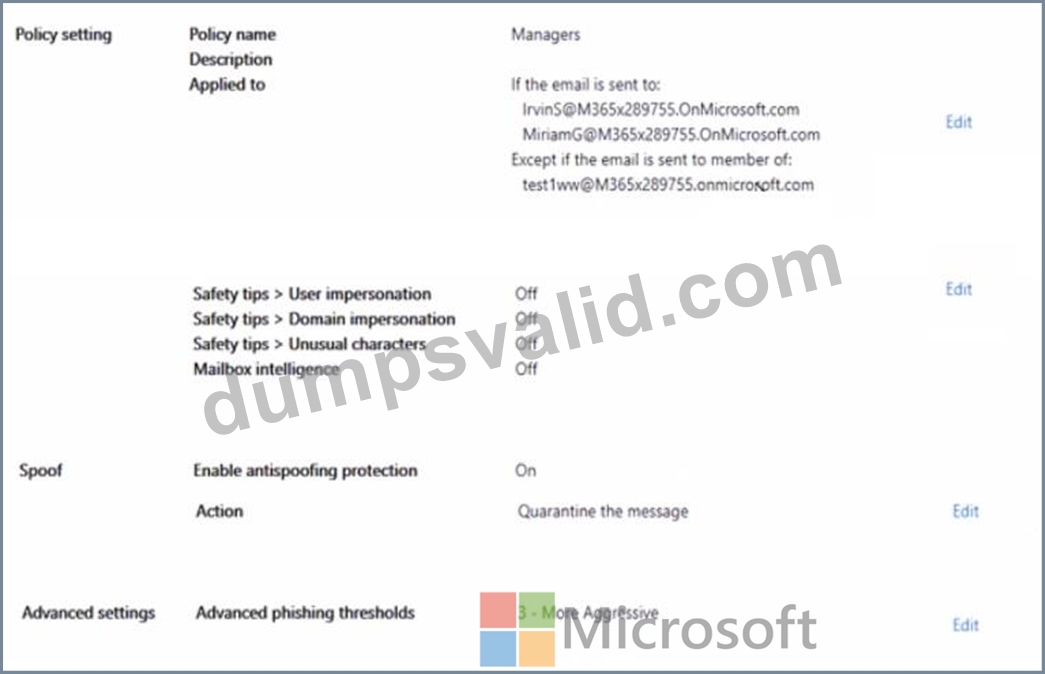
Use the drop-down menus to select the answer choke that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.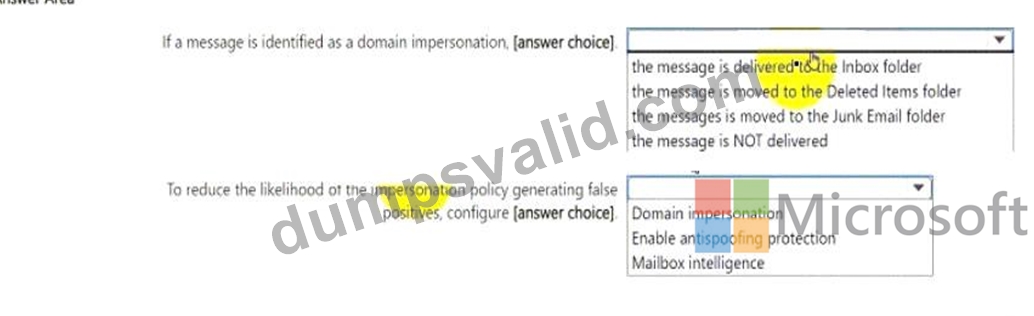
Answer:
Explanation: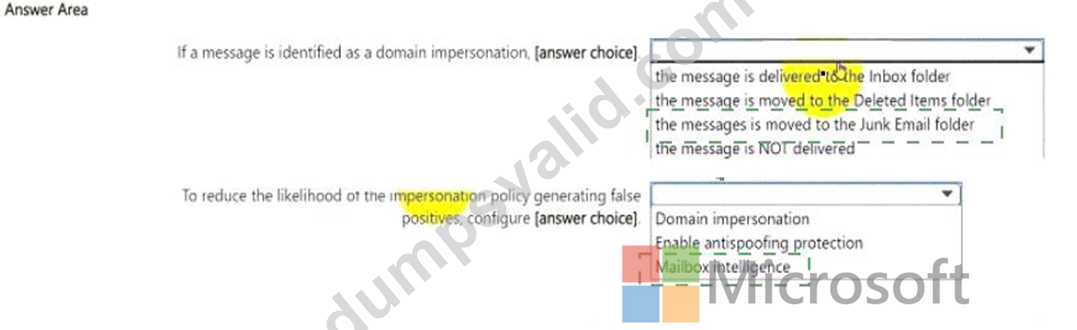
Explanation:
If a message is identified as a domain impersonation: the message is moved to the Junk Email folder According to the anti-phishing policy settings shown in the exhibit, messages identified as domain impersonation should be moved to the Junk Email folder to reduce the risk of phishing attacks.
To reduce the likelihood of the impersonation policy generating false positives, configure: Mailbox intelligence Mailbox intelligence helps in reducing false positives by using machine learning and historical email patterns to make better decisions about which emails are legitimate and which are not.
NEW QUESTION # 238
You implement Microsoft Azure Advanced Threat Protection (Azure ATP).
You have an Azure ATP sensor configured as shown in the following exhibit.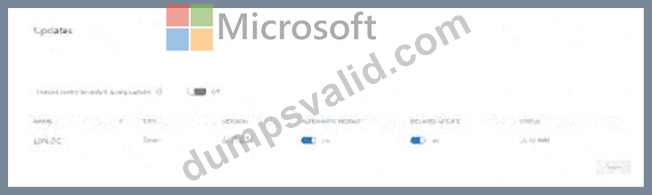
How long after the Azure ATP cloud service is updated will the sensor update?
- A. 20 hours
- B. 12 hours
- C. 48 hours
- D. 7 hours
Answer: B
NEW QUESTION # 239
You have an Azure AD tenant and a Microsoft 365 E5 subscription. The tenant contains the users shown in the following table.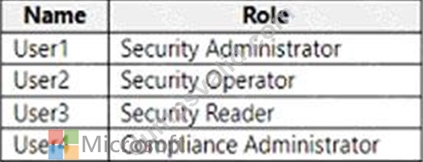
You plan to implement Microsoft Defender for Endpoint.
You verify that role-based access control (RBAC) is turned on in Microsoft Defender for Endpoint.
You need to identify which user can view security incidents from the Microsoft 365 Defender portal.
Which user should you identify?
- A. User2
- B. User1
- C. User3
- D. User4
Answer: B
NEW QUESTION # 240
You have a Microsoft 365 tenant that contains 1,000 iOS devices enrolled in Microsoft Intune. You plan to purchase volume-purchased apps and deploy the apps to the devices. You need to track used licenses and manage the apps by using Intune. What should you use to purchase the apps?
- A. Apple Business Manager
- B. Apple iTunes Store
- C. Apple Configurator
- D. Microsoft Store for Business
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/vpp-apps-ios
NEW QUESTION # 241
HOTSPOT
You have a Microsoft 365 E5 subscription.
All company-owned Windows 11 devices are onboarded to Microsoft Defender for Endpoint.
You need to configure Defender for Endpoint to meet the following requirements:
Block a vulnerable app until the app is updated.
Block an application executable based on a file hash.
The solution must minimize administrative effort.
What should you configure for each requirement? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.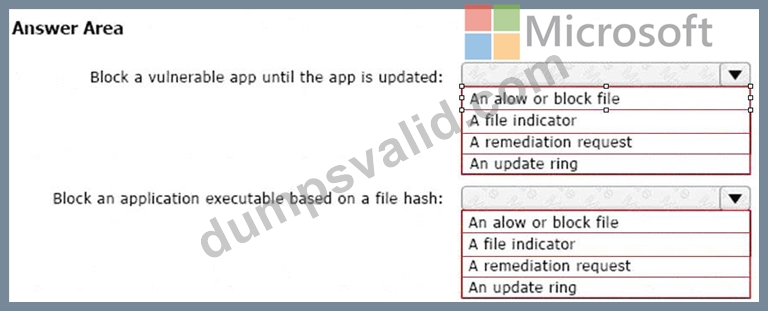
Answer:
Explanation: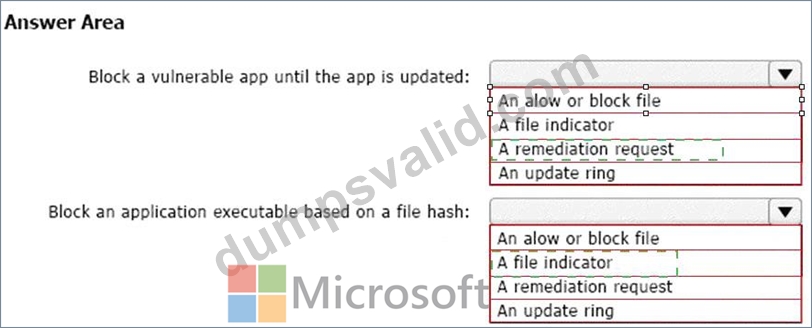
Explanation: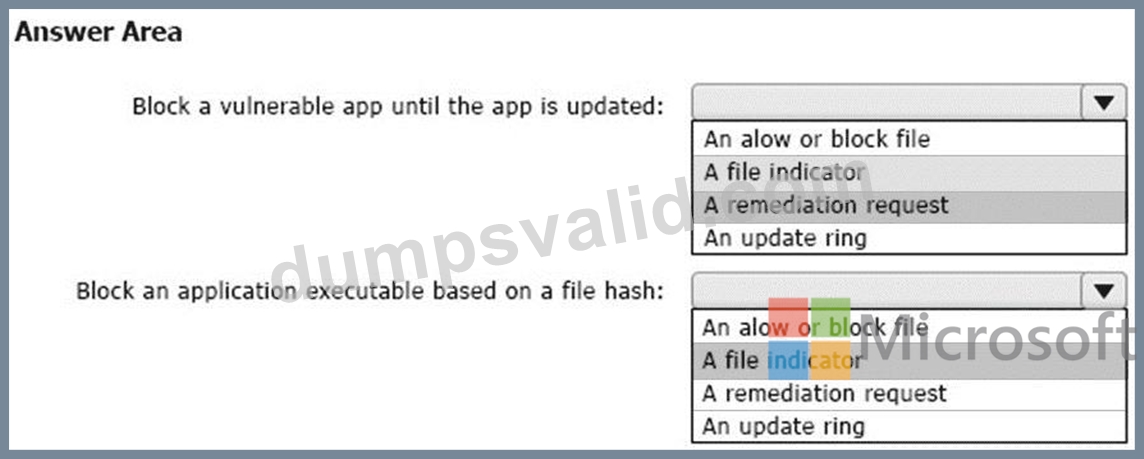
Box 1: A remediation request
Block a vulnerable app until the app is updated.
Block vulnerable applications
How to block vulnerable applications
Go to Vulnerability management > Recommendations in the Microsoft 365 Defender portal.
Select a security recommendation to see a flyout with more information.
Select Request remediation.
Select whether you want to apply the remediation and mitigation to all device groups or only a few.
Select the remediation options on the Remediation request page. The remediation options are software update, software uninstall, and attention required.
Pick a Remediation due date and select Next.
Under Mitigation action, select Block or Warn. Once you submit a mitigation action, it is immediately applied.
Review the selections you made and Submit request. On the final page you can choose to go directly to the remediation page to view the progress of remediation activities and see the list of blocked applications.
Box 2: A file indicator
Block an application executable based on a file hash.
While taking the remediation steps suggested by a security recommendation, security admins with the proper permissions can perform a mitigation action and block vulnerable versions of an application. File indicators of compromise (IOC)s are created for each of the executable files that belong to vulnerable versions of that application. Microsoft Defender Antivirus then enforces blocks on the devices that are in the specified scope.
The option to View details of blocked versions in the Indicator page brings you to the Settings > Endpoints > Indicators page where you can view the file hashes and response actions.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/security/defender-vulnerability-management/tvm-block-vuln- apps
NEW QUESTION # 242
HOTSPOT
You have a Microsoft 365 E5 subscription.
From Azure AD Privileged Identity Management (PIM), you configure Role settings for the Global Administrator role as shown in the following exhibit.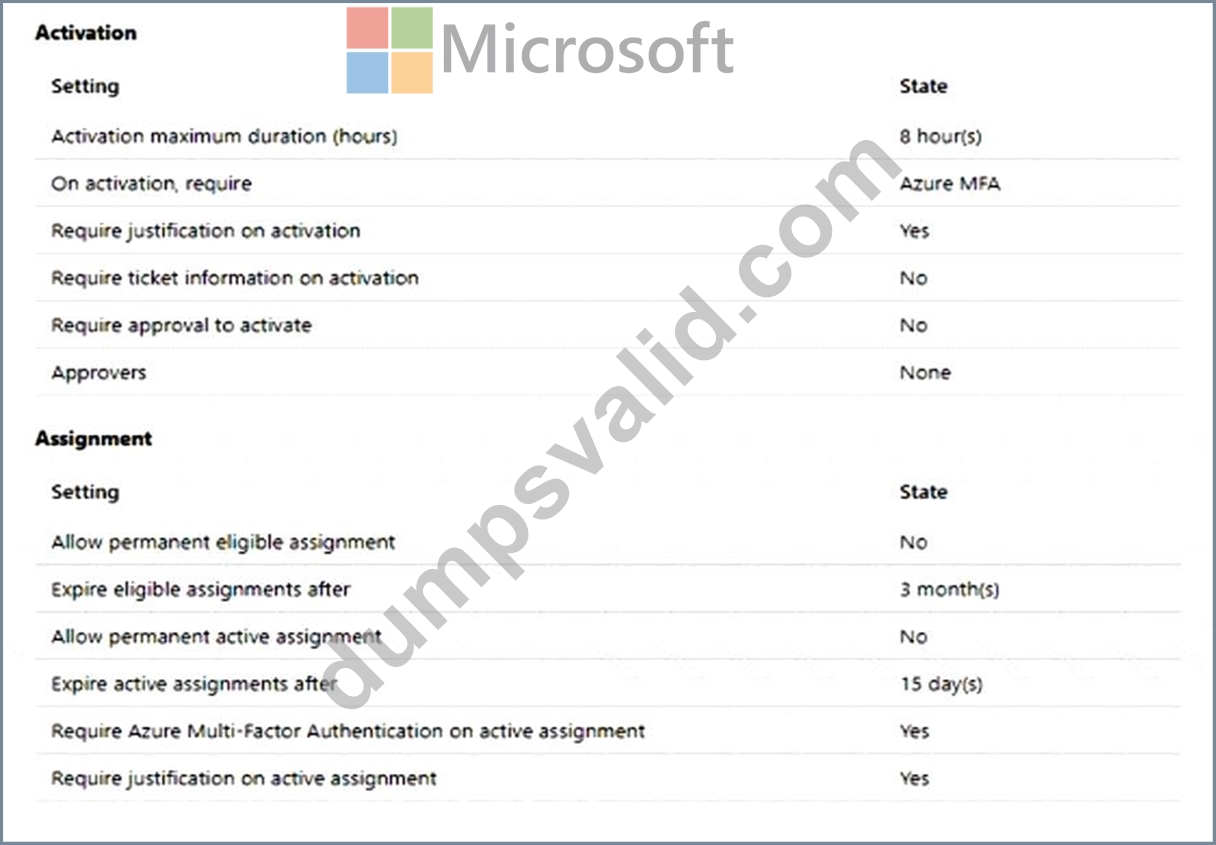
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.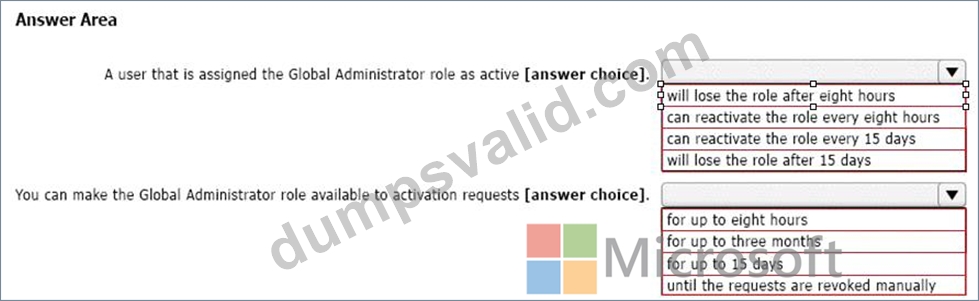
Answer:
Explanation: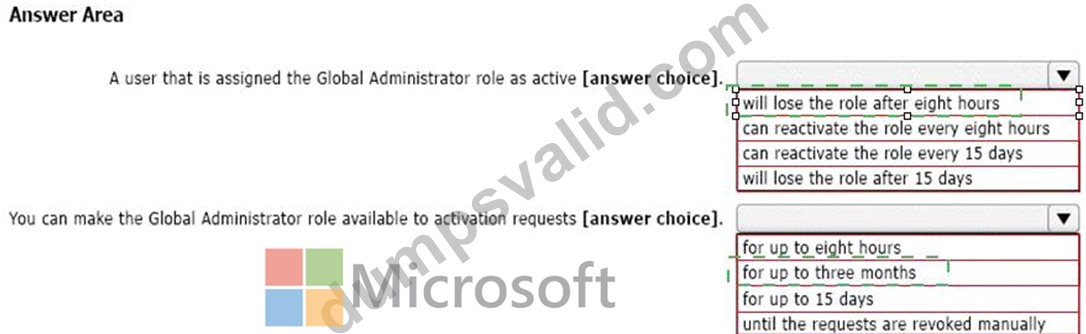
Explanation: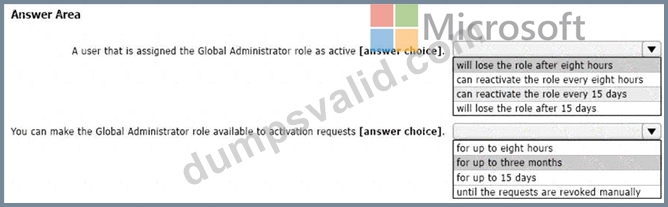
Box 1: will lose the role after eight hours
From exhibit: Activation, Activation maximum duration (hours): 8 hour(s) Box 2: for up to three months We see from exhibit: Assignment, Expire eligible assignment after: 3 month(s)
NEW QUESTION # 243
You have a Microsoft 365 subscription.
Your network uses an IP address space of 51.40.15.0/24.
An Exchange Online administrator recently created a role named Role1 from a computer on the network.
You need to identify the name of the administrator by using an audit log search.
For which activities should you search and by which field should you filter in the audit log search? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.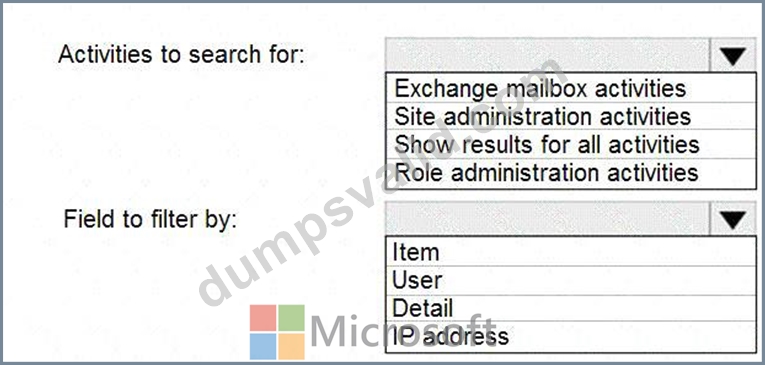
Answer:
Explanation: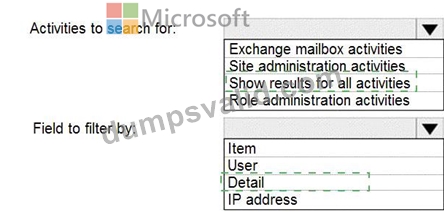
Explanation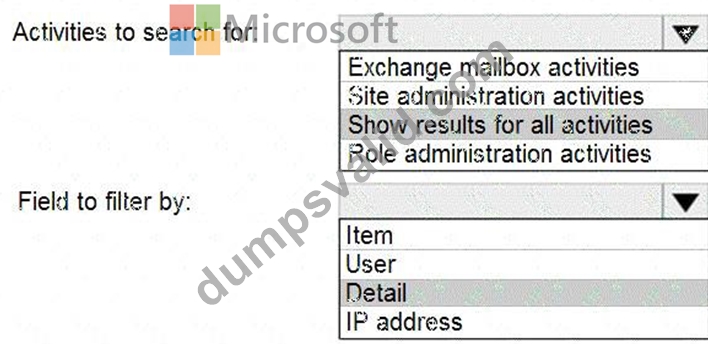
NEW QUESTION # 244
You have a Microsoft 365 E5 tenant that contains the devices shown in the following table.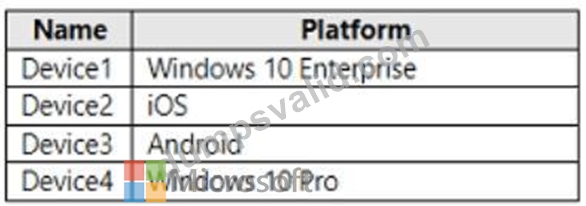
The devices are managed by using Microsoft Intune.
You plan to use a configuration profile to assign the Delivery Optimization settings.
Which devices will support the settings?
- A. Device1, Device2, Device3, and Device4
- B. Device1 and Device4
- C. Device1, Device3, and Device4
- D. Device1 only
Answer: D
NEW QUESTION # 245
You have a Microsoft 365 ES subscription that has three auto retention policies as show in the following exhibit.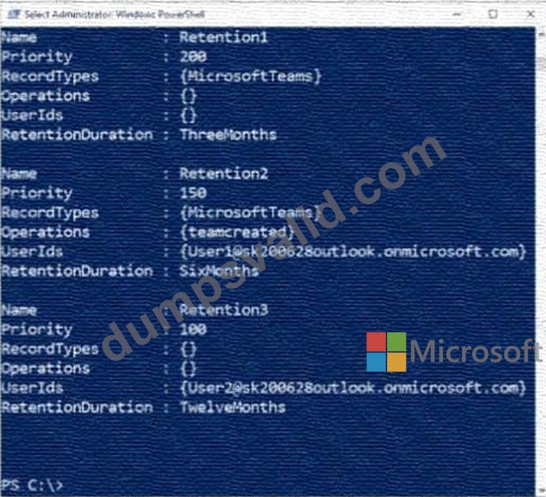
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic NOTE Each correct selection is worth one point.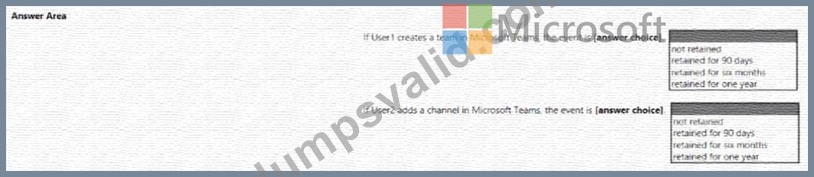
Answer:
Explanation: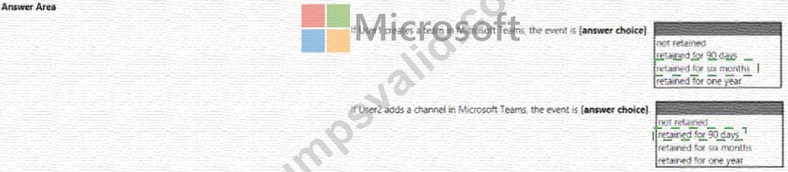
Explanation: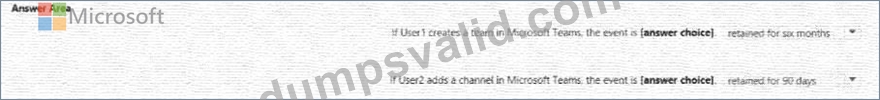
NEW QUESTION # 246
Youi network contains an Active Directory domain.
You have a Microsoft Entra tenant that has Security defaults disabled.
Microsoft Entra Connect Sync is configured for directory synchronization. Password hash synchronization and pass-through authentication are disabled.
You need to enable Microsoft Entra ID Protection to detect leaked credentials.
What should you do first?
- A. From Microsoft Entra Connect, enable pass-through authentication.
- B. From the Microsoft Entra admin center, configure verifiable credentials.
- C. From Microsoft Entra Connect, enable password hash synchronization.
- D. From the Microsoft Entra admin center, enable Security defaults.
Answer: C
NEW QUESTION # 247
You have a Microsoft 365 tenant that contains a Windows 10 device named Device1 and the Microsoft Endpoint Manager policies shown in the following table.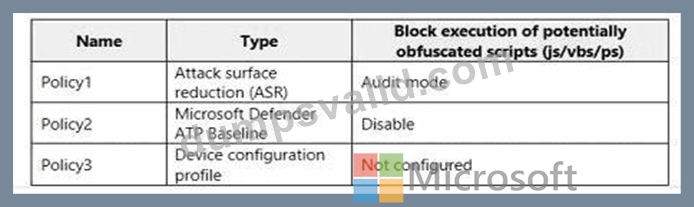
- A. only the settings of Policy!
- B. only the settings of Policy2
- C. no settings
- D. only the settings of Policy3
Answer: D
NEW QUESTION # 248
You implement Microsoft Azure Advanced Threat Protection (Azure ATP).
You have an Azure ATP sensor configured as shown in the following exhibit.
How long after the Azure ATP cloud service is updated will the sensor update?
- A. 20 hours
- B. 12 hours
- C. 48 hours
- D. 7 hours
Answer: B
NEW QUESTION # 249
You have a Microsoft 365 subscription that uses an Azure AD tenant named contoso.com. The tenant contains the users shown in the following table.
From the Sign-ins blade of the Microsoft Entra admin center for which users can User1 and User2 view the sign-ins? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.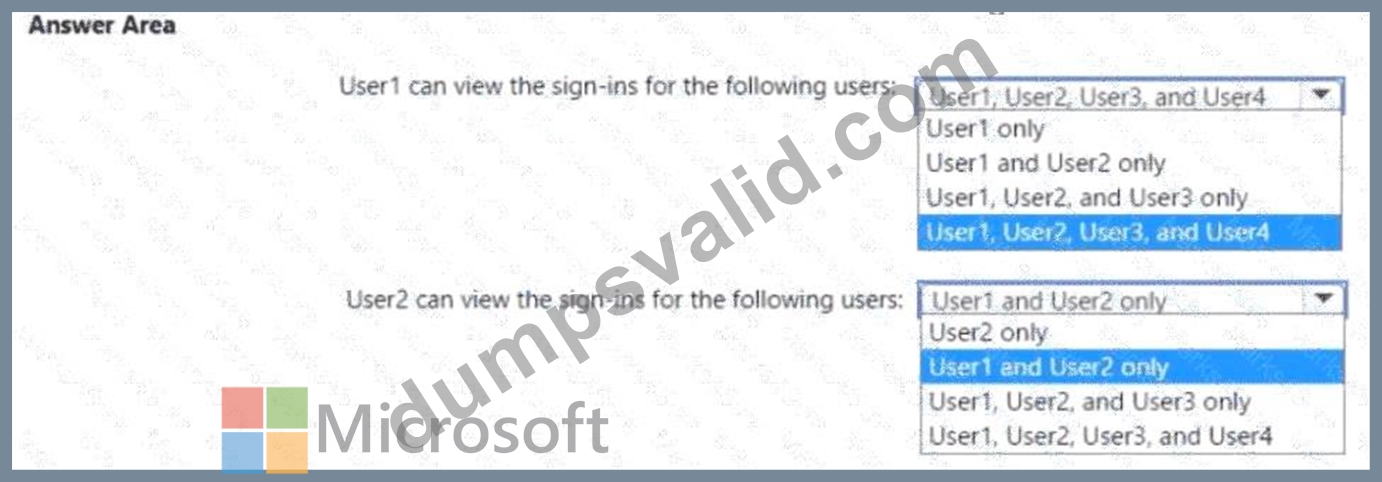
Answer:
Explanation: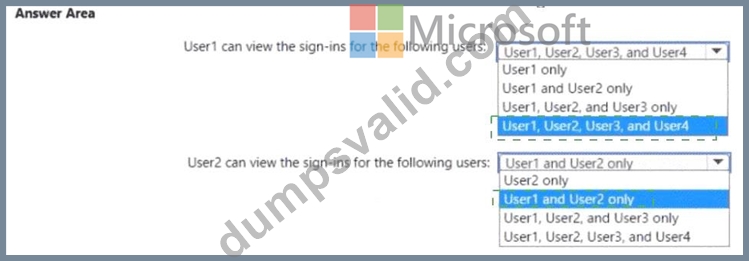
Explanation: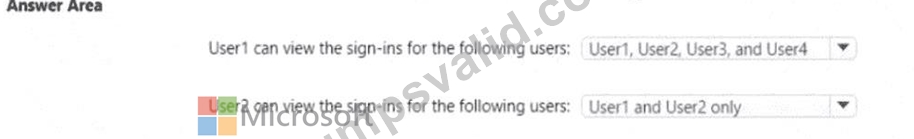
NEW QUESTION # 250
You have a Microsoft 365 E5 tenant.
You have a sensitivity label configured as shown in the Sensitivity label exhibit. (Click the Sensitivity label tab.)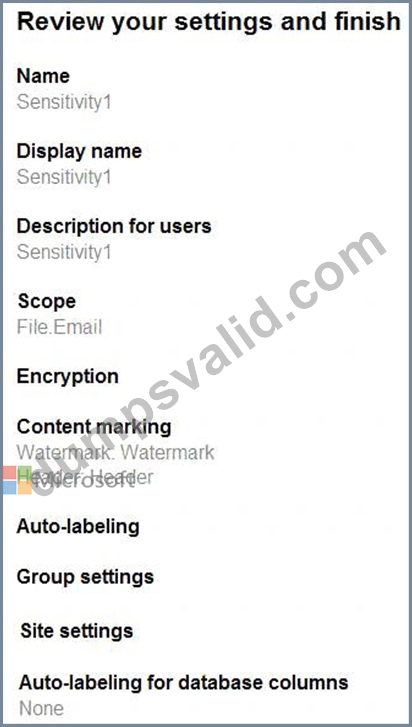
You have an auto-labeling policy as shown in the Auto-labeling policy exhibit. (Click the Auto-labeling policy tab.)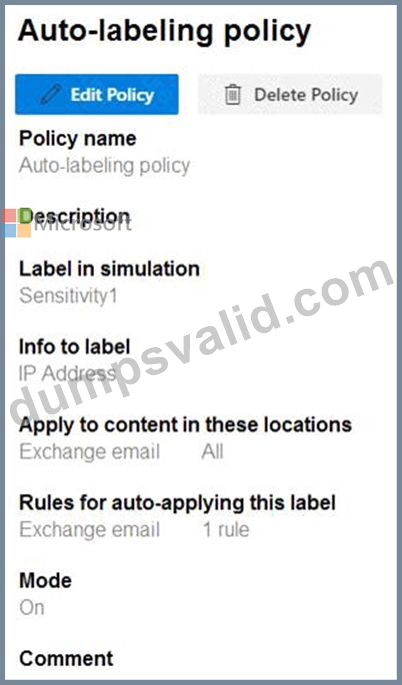
A user sends an email that contains the components shown in the following table.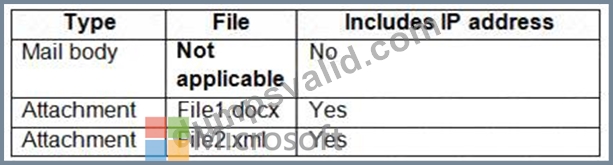
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.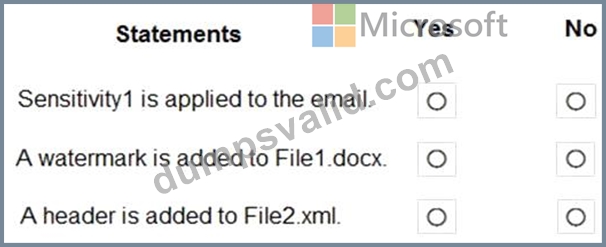
Answer:
Explanation: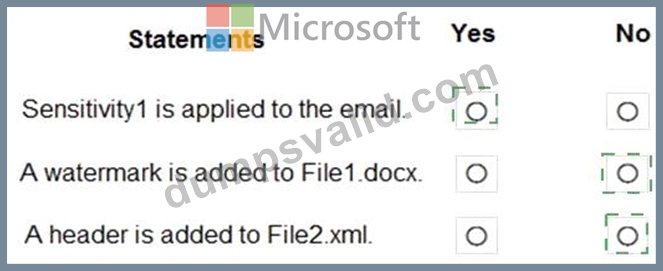
Explanation
Graphical user interface, text, application Description automatically generated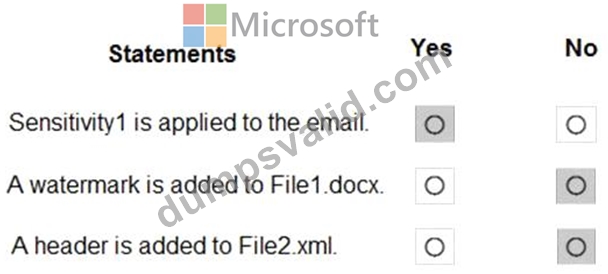
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-wo
NEW QUESTION # 251
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.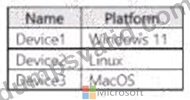
You plan to create an Endpoint security policy by using the Defender Update controls template. To which device can you apply the policy?
- A. Devke1, Device2. and Devke3
- B. Devke1 and Device3 only
- C. Device1 and Devke2 only
- D. Device1 only
Answer: D
NEW QUESTION # 252
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.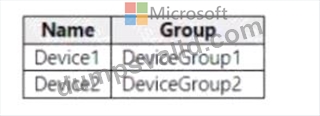
At 08:00. you create an incident notification rule that has the following configurations:
* Name: Notification!
* Notification settings
o Notify on alert seventy: Low
o Device group scope: All (3)
o Details: First notification per incident
* Recipients: [email protected], [email protected]
At 08:02. you create an incident notification rule that has the following configurations:
* Name: Notification
* Notification settings
o Notify on alert severity: Low. Medium
o Device group scope: DevtceGroup1, DeviceGroup2
* Recipients: [email protected]
in Microsoft 365 Defender, alerts are logged as shown in the following table.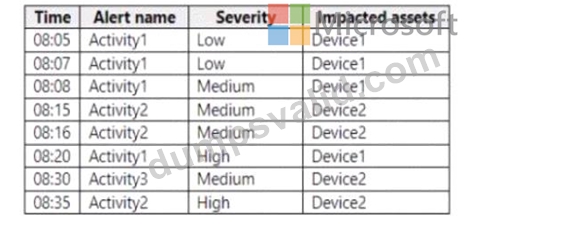
For each of the following statements, select Yes if the statement is true. Otherwise, select No1.
NOTE: Each correct selection is worth one point.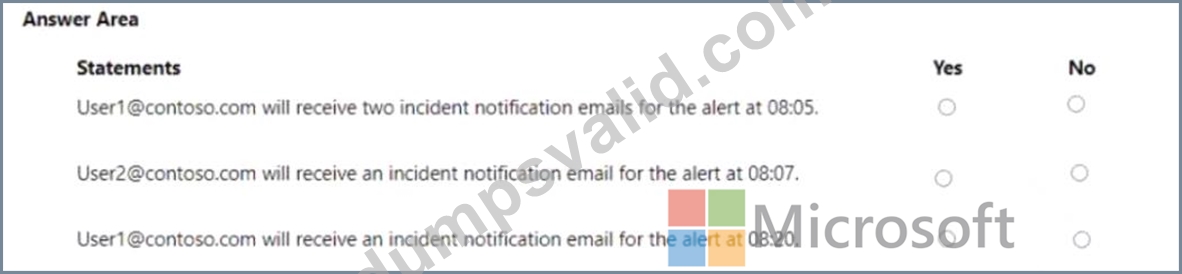
Answer:
Explanation: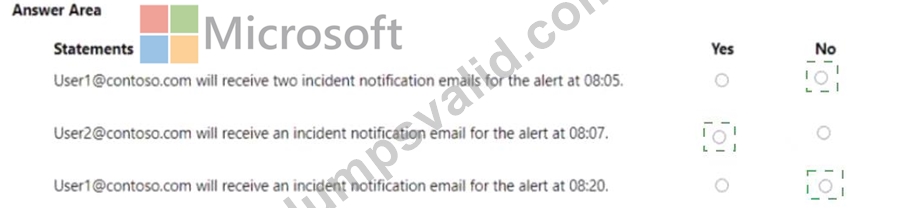
Explanation: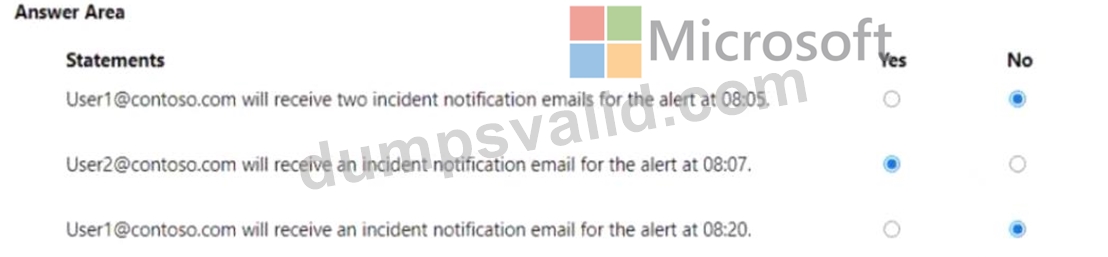
NEW QUESTION # 253
HOTSPOT
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.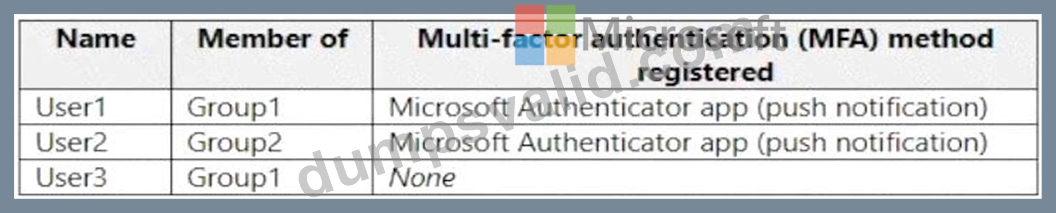
You configure the Microsoft Authenticator authentication method policy to enable passwordless authentication as shown in the following exhibit.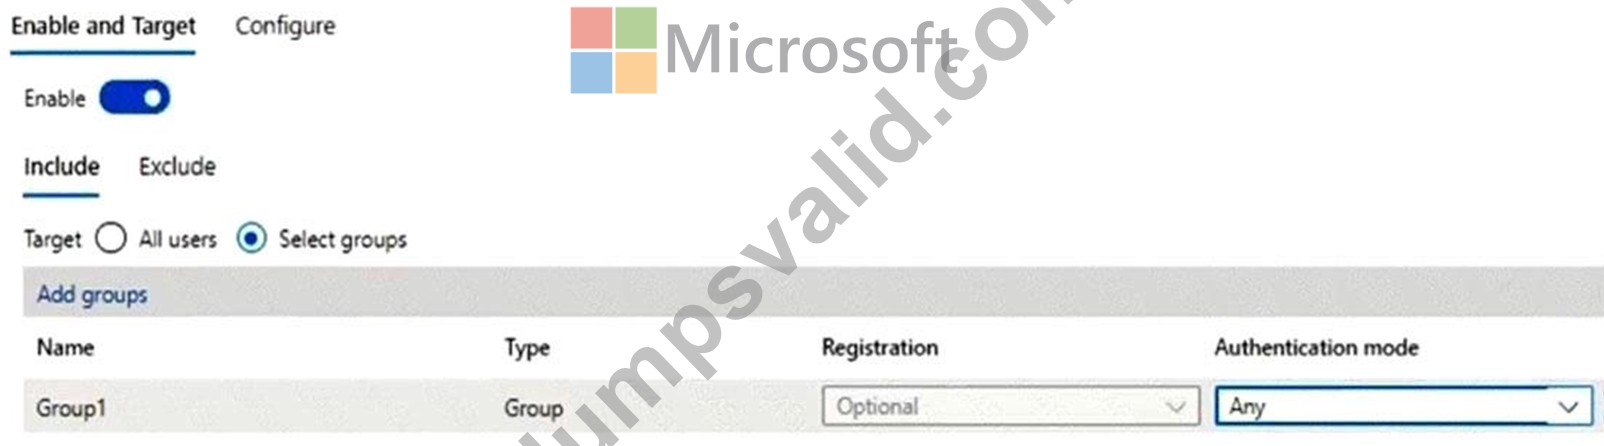
Both User1 and User2 report that they are NOT prompted for passwordless sign-in in the Microsoft Authenticator app.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.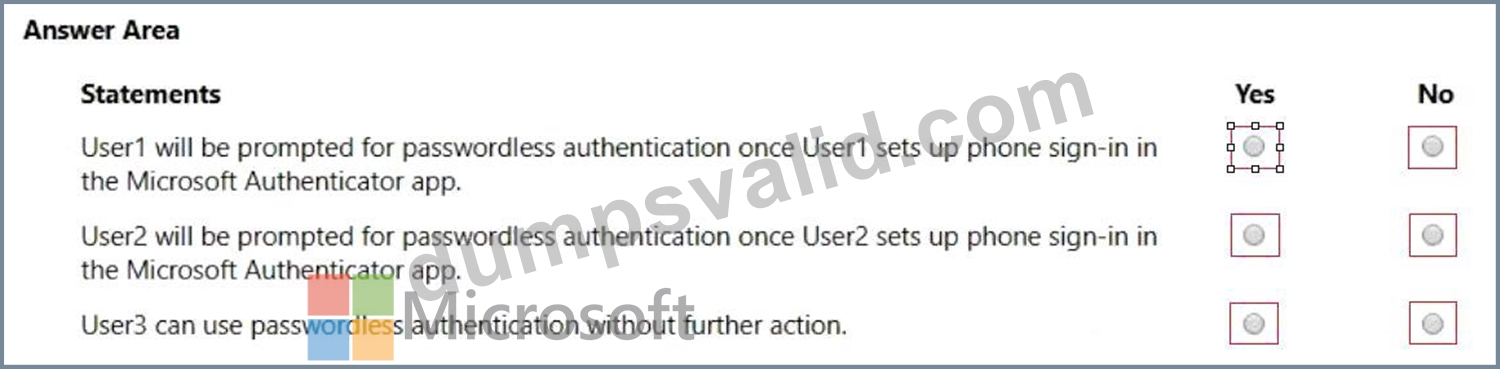
Answer:
Explanation: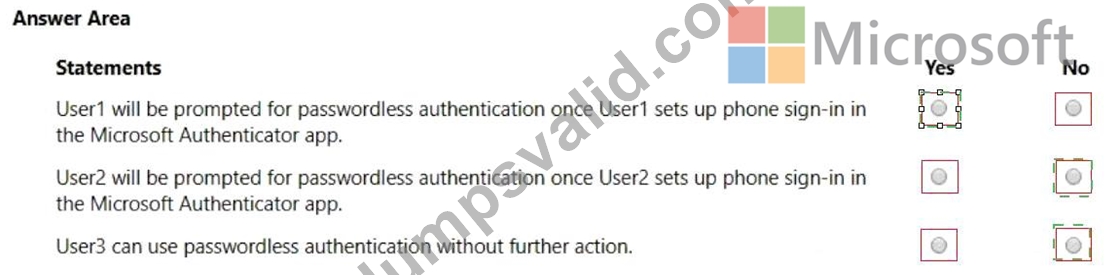
Explanation: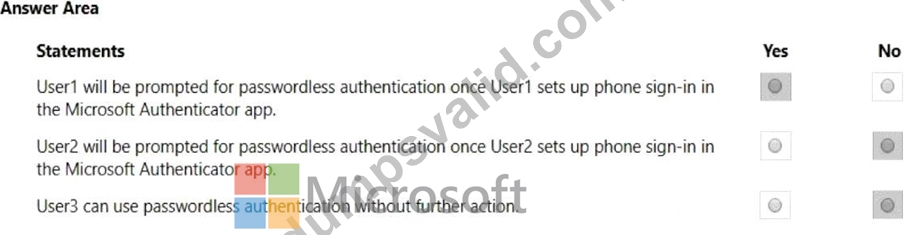
Box 1: Yes
User1 is member of Group1.
User1 has MFA registered method of Microsoft Authenticater app (push notification) The Microsoft Authenticator authentication method policy is configured for Group1, registration is optional, authentication method is any.
Note: Microsoft Authenticator can be used to sign in to any Azure AD account without using a password.
Microsoft Authenticator uses key-based authentication to enable a user credential that is tied to a device, where the device uses a PIN or biometric. Windows Hello for Business uses a similar technology.
This authentication technology can be used on any device platform, including mobile. This technology can also be used with any app or website that integrates with Microsoft Authentication Libraries.
Box 2: No
User2 is member of Group2.
The Microsoft Authenticator authentication method policy is configured for Group1, not for Group2.
Box 3: No
User3 is member of Group1.
User3 has no MFA method registered.
User3 must choose an authentication method.
Note: Enable passwordless phone sign-in authentication methods
Azure AD lets you choose which authentication methods can be used during the sign-in process. Users then register for the methods they'd like to use.
Reference:
https://learn.microsoft.com/en-us/azure/active-directory/authentication/howto-authentication-passwordless- phone
NEW QUESTION # 254
You have a Microsoft 365 subscription.
You integrate Microsoft Defender for Cloud Apps with Microsoft Defender for Endpoint.
You need to create a policy to block users from accessing discovered apps that have a risk score of 4 or lower.
Which two settings should you configure? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.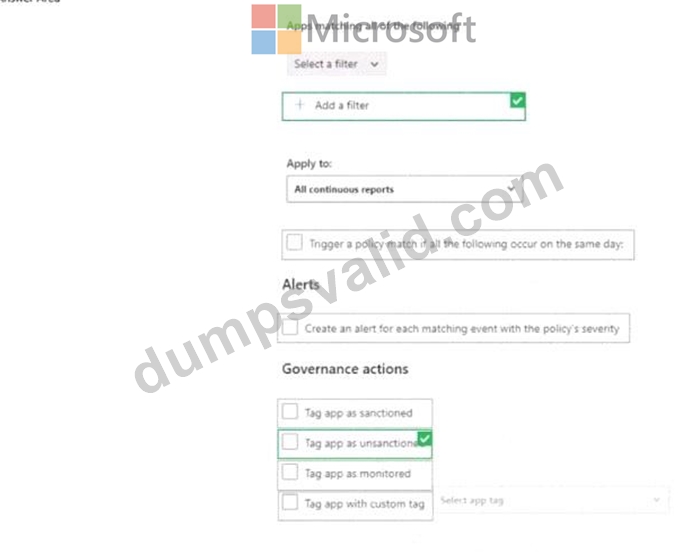
Answer:
Explanation: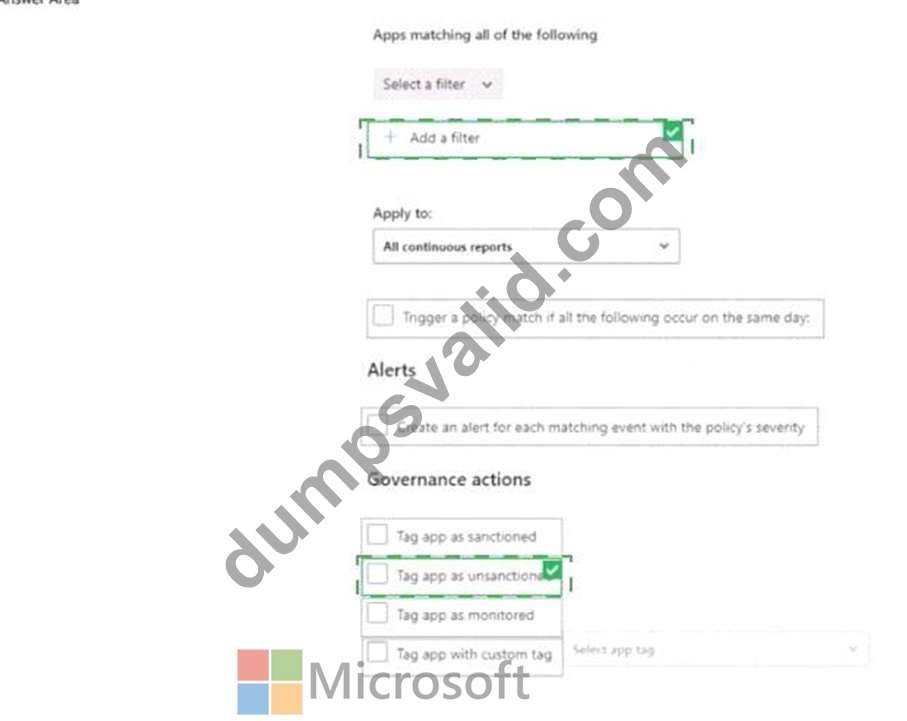
Explanation:
NEW QUESTION # 255
......
Microsoft MS-102 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Start your MS-102 Exam Questions Preparation: https://www.dumpsvalid.com/MS-102-still-valid-exam.html
A Fully Updated MS-102 Exam Dumps - PDF Questions and Testing Engine: https://drive.google.com/open?id=1bDp9aUuC8mw5iE4YY7ubJCAsFZgQRy5L